

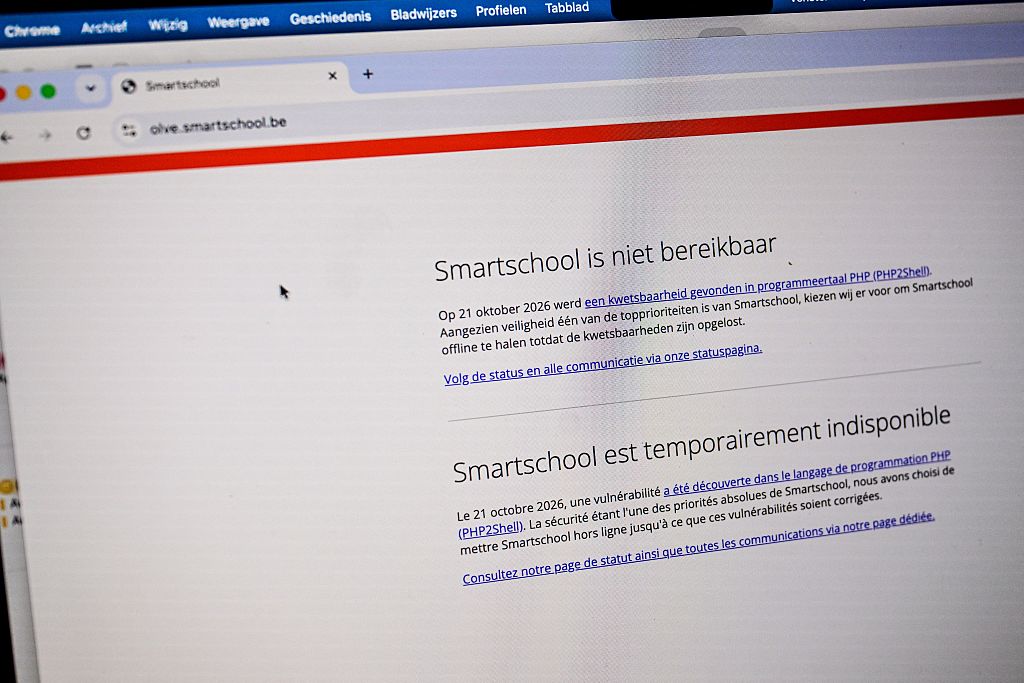
On Wednesday, an open-source networking technology that has been around for decades, PHP, nearly brought the internet to a halt. The reason was that two vulnerabilities, which had remained undiscovered for many years, were recently identified by researchers as exploitable.
These two vulnerabilities are referred to as PHP2Shell, with official codes CVE-2026-109618 and CVE-2026-109619. In simple terms, these vulnerabilities allow anyone who knows how to exploit them to invade online systems running PHP, such as websites or internet-facing servers, without the need for a password, and to access or modify the data within them.
In terms of the severity of the situation, this incident was quite significant, forcing millions of people around the world to rush to patch their systems before malicious hackers could take advantage of them.
PHP Foundation, responsible for maintaining the PHP network software, publicly released a fix patch on Wednesday. Once installed, this patch can prevent network-facing servers from being attacked. The foundation had previously provided some of the largest internet companies and website hosting providers that rely on PHP with the opportunity to apply the fix in advance.
Thanks to weeks of behind-the-scenes communication and careful coordination within the industry, the world has so far largely avoided large-scale exploitation of the internet. Starting from Wednesday, governments around the world began urging citizens and businesses with websites to take action to reduce their own risks. Banks, retailers, gaming websites, online stores, hospitals, and some government agencies have all shut down their servers to prevent attacks.
However, security researchers warn that the matter is not over yet, as there are still a large number of systems around the world that have not been patched and are therefore vulnerable to intrusion and data theft.
This is also likely not to be the last major internet software crisis. Some people predict that with the emergence of artificial intelligence, more vulnerabilities that have not yet been identified, are waiting to be discovered, and could be exploited will be quickly identified.
What happened?
Security researchers from Calif have discovered two vulnerabilities in PHP. PHP is a programming language widely used worldwide for building websites and web applications, both on the internet and in locally hosted systems within corporate networks, such as intranets and internal websites.
These two vulnerabilities were first discovered in 2024, but at that time they were not considered exploitable, so no patches were applied. Security researchers have recently found ways to exploit them, and have therefore reminded software developers to fix them as soon as possible.
Calif notified PHP Foundation, and the latter immediately began to fix the vulnerability and coordinate its disclosure. By providing relevant information and patches during a strictly confidential ban period—that is, keeping it secret until a specific deadline—the foundation gave large companies the opportunity to install the fix in advance.
Why are these vulnerabilities so serious?
What makes this issue so serious is that it can be exploited remotely over the internet, and victims do not need to click on links or open files. This is known as remote code execution, and it is one of the most destructive types of vulnerabilities, as it can allow hackers anywhere in the world to gain almost complete control over affected, unpatched systems.
Worse still, these specific PHP vulnerabilities allow attackers to invade any unpatched system over the internet without the need for a password or other credentials, a phenomenon known as unauthorized access.
This will enable malicious hackers to implant malware on computers, such as to steal data, or simply to maintain a long-term foothold for future return visits.
Why are 70% of web pages affected?
PHP is just one of many outdated technologies that are still capable of functioning properly. These technologies have undergone multiple rounds of evolution and generational replacements throughout the development of the internet, and today they are ubiquitous, almost acting as the "glue" that holds the internet together. In many cases, these tools are developed by open-source maintainers who do not receive any compensation for their work, and as a result, they cannot afford third-party security audits. Yet, enterprises rely heavily on these projects without providing them with financial support.
Were these vulnerabilities discovered by artificial intelligence?
The security researchers from Calif were recognized for discovering these vulnerabilities during a security audit of the code for PHP earlier this year. Calif participated in the Hack the Planet initiative launched by OpenAI and cloud security giant Wiz; the latter subsequently verified the proof-of-concept exploit code created by Calif.
In the explanatory article for Calif (which also comes with a comic – great, worth a look), researchers explained that artificial intelligence was used to assist in exploiting this vulnerability, but most of the work still relied on the researchers' existing knowledge, as well as their familiarity with the PHP codebase and the history of vulnerability exploits.
Calif writes: 'There is no model that can directly uncover 'all vulnerabilities' with just simple hints. At least not yet.'
Why were these vulnerabilities exploited before they were disclosed?
Despite efforts by all parties to keep the details of the vulnerability confidential until Wednesday, it appears that PHP2Shell had already been exploited before the patch was released.
Due to its large scale and high visibility, Amazon has a great deal of insight into online threats. In a blog post, the company stated that it detected signs of the exploitation of PHP2Shell about a week before the release of patch PHP, indicating that someone somewhere already knew how to exploit these vulnerabilities before the details of the flaws were widely made public. Amazon said that it is not yet clear how hackers became aware of these vulnerabilities, but defenders should look back to October 17th for evidence of exploitation.
There are several accounts of how the incident unfolded. Once the vulnerabilities are patched, the details of the patches may become immediately apparent, especially in open-source code like PHP, which can be viewed publicly by anyone. Taking advantage of these vulnerabilities may not be easy, but knowing where the vulnerabilities are and how they were fixed could help malicious hackers determine their attack targets and exploit the code.
It is also possible that there was a leak somewhere during the ban period, or that communication was interrupted. Open-source communities are vast in scale, and controlling information in this manner relies on the honest cooperation of all parties.
Additionally, it is also possible that hackers discovered these vulnerabilities independently in advance, or learned about them through espionage activities.
Researchers say that it requires a lot of work to actually exploit these vulnerabilities, and weaponizing them has always been a challenge – but not impossible – which also explains why we haven’t seen any large-scale exploitation scenarios to this day.
The internet has experienced widespread downtime, but it is now beginning to recover. Have we managed to avoid the worst?
It's still too early to draw conclusions, but at present, there are no signs of large-scale exploitation, which is at least an encouraging sign – however, we are not yet completely out of the danger zone.
The CEO of a cybersecurity and monitoring company, Cloudflare, Matthew Prince, stated this week that the company has observed an exponential increase in attempts to exploit these vulnerabilities since they were disclosed. This also indirectly indicates how quickly malicious actors are attempting to take advantage of these flaws for their own gain.
PHP is not only used in Web servers, but also in development tools, command-line and terminal software packages, as well as other software components used in routers, storage devices, and enterprise security devices (such as firewalls and VPN).
It is foreseeable that the utilization of PHP2Shell will continue to appear in the future, as smaller IT teams and individual developers may update more slowly. At the same time, many companies that have integrated PHP into their own products and software also need to make updates, which will involve a transition period.
As more and more devices and systems are updated, the attack surface will gradually shrink. However, the cascading effects of these vulnerabilities may continue for many years, especially in those legacy systems that cannot be updated.
Will this situation happen again?
In the years I have worked as a security journalist, this has been one of those rare occasions when the internet came to a near standstill. In 2016, a massive botnet launched a DDoS attack on the internet registration authority Dyn, causing a large number of top-tier websites to cease service almost completely. In 2017, North Korea used leaked hacking tools from the U.S. government to infect the British healthcare system and deploy ransomware. In 2024, a malfunction in an update to CrowdStrike triggered a global-scale outage, resulting in most computers around the world, including Windows, crashing simultaneously.
From all aspects, with the help of PHP2Shell, the internet has managed to avoid a day that could have been extremely painful and highly destructive. However, this is unlikely to be the last major event to affect the internet in the future, and it may instead mark the beginning of a series of incidents that take advantage of lingering technical vulnerabilities. To a large extent, this is because these old but ubiquitous software programs have inherent flaws that have not yet been discovered, and artificial intelligence tools have made it easier to identify these vulnerabilities.
Like other web programming languages and technologies from several decades ago, PHP is considered "memory-insecure" software, which means it is susceptible to a range of vulnerabilities that can lead to the leakage or overflow of sensitive data from memory storage. The National Security Agency (NSA) of the United States states that approximately 75% of currently exploited vulnerabilities take advantage of memory-related flaws, indicating that hackers frequently utilize such vulnerabilities.
This has prompted the industry to shift towards using memory-safe languages, such as Python, Rust, and Swift. These languages are not as prone to abuse as memory vulnerabilities. As a result, they are largely immune to the numerous vulnerabilities that still affect their predecessors.
But this still leaves a considerable portion of the internet running PHP, media and video codecs, compression libraries, and other software from decades ago – and when these technologies encounter problems, it can have a huge impact on the entire network.