

On October 29, 2026, Binance encountered a major security vulnerability involving unauthorized transfer of cryptocurrencies, with an estimated amount of $6.3 billion. This incident affected multiple blockchain networks and triggered collaborative efforts across the industry to track and freeze the stolen assets.
An initial investigation by Binance indicates that the laptop of an engineer with the username DevOps may have been compromised, which could have served as the entry point for this incident. The exchange stated that there is currently no evidence of any leakage of wallet private keys and pledged to cover all losses through its User Security Asset Fund (SAFU) and company funds.
1. How the event began
On October 29th, a blockchain monitoring system detected suspicious fund movements related to Binance-related wallets. The initial investigation focused on Ethereum-based transfers, but subsequent analysis revealed that the activities also involved Bitcoin, Tron, Solana, XRP Ledger, and other networks as well.
As investigators traced more transactions, the estimated amount affected continued to rise, with Binance itself providing an estimate of $6.3 billion.
This incident quickly evolved into a cross-chain investigation, with blockchain intelligence companies and cryptocurrency enterprises all assisting in identifying affected wallets and preventing further transfer of assets.
2. How the attackers are alleged to have infiltrated Binance
Suspected entry point
An initial investigation by Binance indicates that a laptop belonging to an engineer with the identifier DevOps may have been compromised, allowing the attacker to gain access to an internal service container. This access could have been utilized to submit unauthorized withdrawal transactions.
As of now, it has not been publicly confirmed how the devices were compromised. Binance also stated that there is no evidence indicating that the wallet private keys were leaked.
Why might unauthorized withdrawals occur?
Preliminary results indicate that the attackers may have exploited access to an authorized internal service, rather than directly stealing wallet private keys.
This distinction is very important because the withdrawal of cryptocurrencies relies on multiple interconnected systems, including internal services, access permissions, and transaction signing infrastructure. Breaching one of these systems could create an opportunity for the misuse of legitimate transaction processes.
The complete process of how the attacker obtained access rights and sufficient privileges is still under investigation.
Ethereum wallet technology
Independent blockchain security analysis has found that in this attack on Binance's Ethereum hot wallets, the Ethereum’s EIP-7702 account delegation mechanism was utilized.
EIP-7702 Allows accounts outside of Ethereum to delegate certain execution functions to smart contract code. Relevant activities indicate that this mechanism may be abused, thereby facilitating unauthorized asset transfers.
This does not mean that Ethereum itself has been compromised. The specific function of this mechanism and how it was exploited still need to be confirmed through Binance's technical review.
3. Scale and timeline of the attack
Blockchain analysis released on October 30 provided a preliminary overview of the development of this event.
The timeline reflects the disclosed on-chain activities and company updates. The final sequence of events is still to be confirmed through forensic investigation.
4. Which cryptocurrencies are affected?
This incident involves various cryptocurrencies, stablecoins, and digital assets with smaller market capitalizations across multiple blockchain networks.
Main assets identified by blockchain analysis
Other related tokens
Other assets identified in the affected wallets include Wrapped Beacon ETH ( wBETH ), Tether Gold ( XAUt ), Uniswap ( UNI ), Ethena ( ENA ), Pepe ( PEPE ), World Liberty Financial USD ( USD1 ), Chainlink ( LINK ), Aave ( AAVE ), Avalanche ( AVAX ), Optimism ( OP ), USDT0 , Paxos Gold ( PAXG ), Zama ( ZAMA ), and Lagrange , as well as several smaller tokens.
Arkham Intelligence Multiple addresses related to suspected attackers have been identified to assist investigators in monitoring the subsequent flow of funds. As more transactions are identified, the list of tokens may still change.
5. Who hacked Binance?
North Korea
On October 30th, blockchain analysis firm Chainalysis stated that it is highly confident that North Korea is responsible for the Binance incident. Their investigators claimed to have discovered funds from a previous vulnerability exploitation by Bitget that were mixed with the stolen funds from Binance.
These indications point to possible connections with North Korea, but the identities of the responsible persons have not yet been publicly confirmed. Binance stated that they are cooperating with law enforcement authorities to identify the individuals involved and bring them to justice.
Therefore, this attribution should be regarded as an intelligence assessment, rather than a final legal conclusion.
6. How much funds have been frozen and recovered?
Initially, Binance stated that through coordination with blockchain partners, token issuers, and other industry participants, approximately $3 billion in affected assets had been frozen.
Multiple companies and networks have participated in this effort:
- Tether ( USDT ): It is stated that over $1.567 billion related to this incident has been frozen, and subsequent analysis has discovered even more restricted funds distributed across multiple addresses. USDT.
- Circle ( USDC ): Approximately $823 million related to this incident has been frozen. USDC.
- Ripple ( RLUSD ): Confirmed that we are monitoring this incident and are actively freezing the affected funds.
- Arbitrum: Its security committee carried out an action to freeze assets related to this vulnerability exploitation, amounting to approximately $30.5 million.
- Other issuers and partners: Including USD1, FDUSD, and other assets such as gold-linked tokens, they are also subject to freezes or other restrictions.
Why Freezing is Important
Stablecoins such as USDT and USDC can be frozen by the issuers, who have the capability to restrict transfers to specific addresses. This helps to prevent suspected attackers from transferring some of the affected assets.
Bitcoin and Ethereum do not have a centralized issuer with the same ability to maintain an address blacklist. Their recovery relies more on transaction tracking, cooperation from exchanges and intermediaries, as well as legal actions.
It is necessary to distinguish between frozen assets and recovered funds. Frozen cryptocurrencies may still not be available for use until investigators confirm ownership and determine how they should be returned in accordance with the law.
7. Where did the stolen funds go?
Blockchain investigators traced the flow of funds between Ethereum, Bitcoin, Tron, Solana, XRP Ledger, and multiple layer-two networks.
Some assets were converted into other cryptocurrencies through exchanges and transferred between multiple addresses. Disclosed activities include transactions involving Ether and TRX, as well as interactions with decentralized exchanges and other blockchain services.
These movements increase the difficulty of recovery, but the public blockchain records enable investigators to track transactions and identify associations between wallets.
The flow of funds does not necessarily mean that the attacker has successfully cashed out. As of October 30th, the ultimate destination of all affected assets remains unknown.
What happened to Binance customers?
Have customer funds been lost?
Binance stated that customer funds are still safe and pledged to cover all losses through the SAFU fund and company funds. In addition, the exchange is said to have reserved $6.34 billion in company funds to cover the losses incurred in this incident, further demonstrating its commitment to protecting customers.
This commitment is very important to customers, but its implementation still needs to be assessed through the exchange's promised updates to reserve certifications and subsequent disclosures.
Is withdrawal affected?
During a security check, Binance temporarily suspended deposit and withdrawal services.
In the update on October 30th, the exchange stated that recharges had returned to normal, while withdrawals were still suspended due to ongoing security enhancements for the withdrawal service and related addresses. The company expects withdrawals to be resumed within 48 hours.
What about the transaction?
The exchange stated that once the security issues are resolved, these services will be restored. The related restrictions are part of their broader preventive measures.
9. Binance's Response and Industry Support
Binance's response includes both internal security measures and collaboration with companies across the entire cryptocurrency industry.
Zhao Changpeng, co-founder and former CEO of Binance ( CZ ), assured users of the safety of their funds. He also expressed his recognition for the employees who worked overnight to handle the incident and thanked industry participants, including competitors, for their assistance.
He Yi, co-founder and co-CEO of Binance, expressed gratitude for the support of the community and stated that the team is conducting security checks before resuming withdrawals.
The key points of the exchanges' responses include:
- Revoke authorizations related to the affected addresses.
- Temporarily restrict the affected services.
- Cooperate with law enforcement agencies and blockchain intelligence companies.
- Coordinating with token issuers and industry partners to freeze assets.
- Prepare a detailed technical review.
- Publish the updated reserve certificate after the rectification.
Tether, Circle, Ripple, and Arbitrum also participated in the response through asset restrictions and freezing measures. Blockchain intelligence companies continue to track transactions and identify related addresses.
This coordinated action demonstrates that in major security incidents, exchanges, token issuers, blockchain networks, and investigators can work together.
10. Why is this incident important to the broader crypto industry?
This incident highlights the risks associated with privileged employee access rights and the internal withdrawal system.
Even if the wallet private keys are kept secure, compromised internal services can still create opportunities for unauthorized transactions. This means that the security of employees' devices, access permissions, and the withdrawal approval system are just as important as protecting the private keys themselves.
This incident also raises a question: how can exchanges prevent their compromised internal systems from independently approving large withdrawals?
Stricter employee access control, independent transaction verification, withdrawal limits, and real-time monitoring may help to reduce the risk of similar incidents occurring again.
For the broader industry, this incident serves as a reminder that even though the underlying blockchain networks continue to operate normally, exchange security remains a significant risk.
11. Market Impact and Unsolved Issues
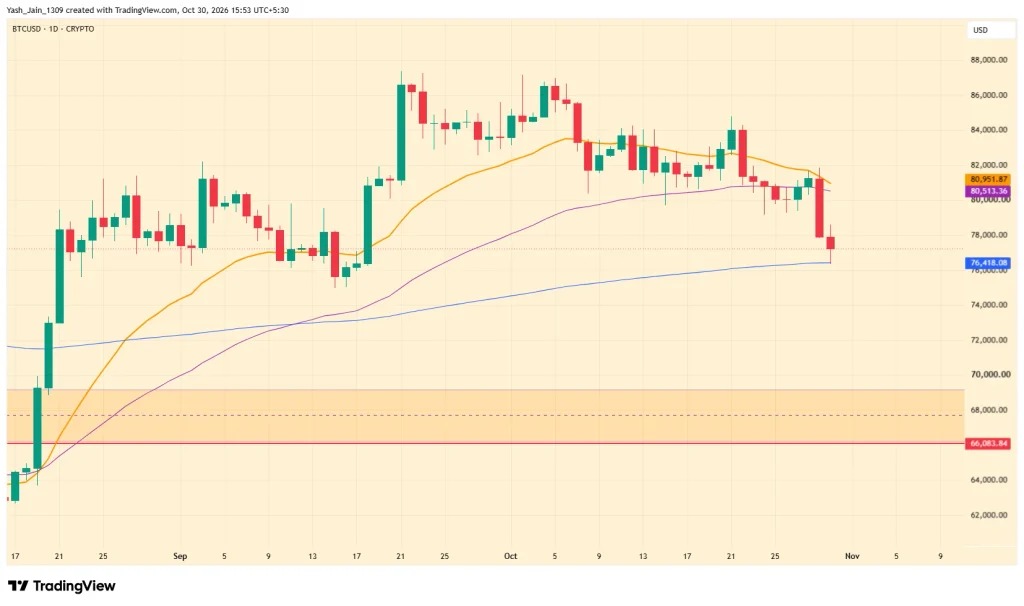
This incident increased the uncertainty in the cryptocurrency market. Reports at the time indicated that Bitcoin fell below $77,000, and Ethereum and other assets also saw declines. Although security concerns may have exacerbated market pressure, price fluctuations cannot be entirely attributed to the Binance incident.
There are still several important questions that remain unanswered:
- DevOps How were engineers' laptops compromised?
- How do attackers obtain sufficient access rights to the withdrawal system?
- How much of the affected cryptocurrencies can ultimately be recovered?
- What attack details will the final technical investigation reveal?
- Will the updated reserve certificate show that customer assets are still fully supported?
- When will all affected services return to normal?
The current top priorities for Binance are to complete security rectifications, resume safe withdrawals, continue to coordinate with investigators, and release a technical review report.
12. Final Evaluation
The Binance incident was a major security failure by a exchange, estimated to have affected approximately $6.3 billion. Preliminary findings indicate that the compromised internal infrastructure may have allowed unauthorized withdrawals without directly leaking wallet private keys.
Approximately $3 billion in assets were coordinated to be frozen, highlighting the importance of industry collaboration in cryptocurrency investigations. However, the final amount recovered, the identities of those who carried out the actions, and the precise methods of the attacks are still subject to investigation.
Binance has promised to bear all losses, which provides some comfort to customers. However, the long-term reputation of the exchange will depend on its ability to safely resume withdrawals, release updated reserve certificates, and provide transparent technical explanations.
This incident should be regarded as a major security vulnerability that is still under investigation, rather than evidence that customer funds have been permanently lost or that all affected assets have been recovered. The final technical report, independently verifiable recovery data, and the restoration of normal service will be the most noteworthy developments.