

Security researchers claim that ClickFix is becoming one of the fastest-growing types of cyberattacks in 2026. It no longer merely disguises itself as "technical repair" pages; instead, it uses web pages and advertisements that look more genuine to trick ordinary users into executing malicious commands on their computers.
The latest case appears in Reddit.
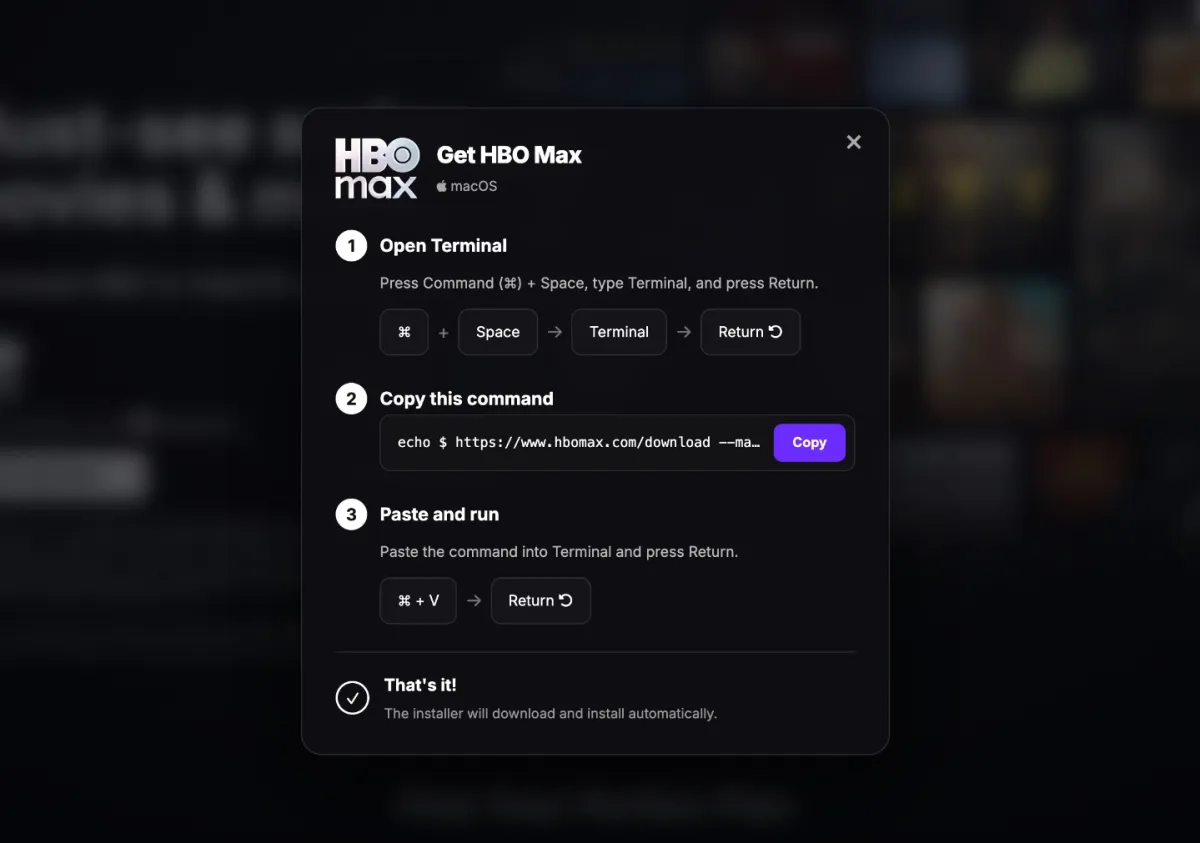
Researchers indicate that the latest round of attacks occurred at Reddit. The attackers utilized compromised official accounts from HBO Max to post a large number of posts that resembled real advertisements, and directed users to a page that impersonated HBO Max.
The page will display a prompt similar to a captcha or an anti-bot checkbox. After the user clicks on it, the page will not directly download the file; instead, it will require the user to complete a so-called “check” and provide a piece of text that needs to be copied and pasted.
Immediately fell for it after execution in the terminal.
The key to this type of attack is that the commands are manually pasted by the user into the system tools for execution. On Windows, the target is usually the command prompt or PowerShell; on macOS, it is Terminal.
Once the user presses Enter, the information-stealing malware is immediately installed. Researchers say that such programs can quickly steal passwords, access rights to logged-in accounts, as well as data from encrypted wallets.
Terminal operations are more difficult to intercept.
Since the operations occur within the system terminal, the attack process is often more difficult to be intercepted in a timely manner by traditional antivirus software or security protection tools. This is also one of the reasons why ClickFix has spread more rapidly recently.
It is not uncommon for developers to execute single-line commands in the terminal on a daily basis, but such operations are not common for ordinary users. It is precisely for this reason that attack pages often take advantage of prompts such as "verify," "repair," or "continue access" to lower users' vigilance.
Security researcher Kevin Beaumont stated that enterprises managing a large number of Windows devices can restrict access to tools such as the Command Prompt and PowerShell across the entire domain, in order to reduce the potential for such attacks to be exploited.
Additional information:Ars Technica mentions that macOS users can utilize tools such as BlockBlock to identify and intercept attack behaviors that attempt to induce users to perform malicious operations on their own.