The ExploitTotal.ai platform currently has over 200 exploitable vulnerabilities generated by AI listed, of which more than 70% of these vulnerabilities did not previously have any known available proof-of-concept ( PoC ).
New York, November 11, 2026 / PRNewswire / -- Anyday Security is a startup dedicated to building a defense layer for the era of attackers targeting AI. Today, the company launched ExploitTotal.ai, a free platform that shows defenders which vulnerabilities open-weight AI models can easily exploit. It also provides security professionals with verified, compliant, and operational PoC for free, allowing them to test whether they are exposed and to establish detection rules.
In the past, transforming patches into usable attack vectors was a slow and highly specialized task. According to Anthropic, cutting-edge AI models are now capable of creating exploitable vulnerabilities within an hour of a patch being released, and this capability is no longer limited to strictly controlled models. GLM-5.3 has been described by the U.S. Government’s Center for Artificial Intelligence Standards and Innovation as the most powerful open-weight model for cyberattacks to date; it can create exploit code end-to-end with almost no substantial protective measures in place at the time of release, and researchers have a success rate of between 64% and 100% in bypassing these protections.
Recent major security incidents, such as PHP2Shell — where attackers attempted to exploit relevant vulnerabilities before patches were released — indicate that the risk of aggressive AI attacks is no longer merely theoretical. Security teams need to respond more quickly.
Anyday Security CEO and Co-founder Yonatan Gorfung stated: " AI has significantly reduced the time between a vulnerability being discovered and it being available for exploitation. In the past 20 years, 'no public exploits' usually meant that such exploits likely did not exist at all. Today, it simply means that no one has made them publicly available yet. In the past, building an exploitable vulnerability often required national-level actors or top researchers to spend weeks on it. Now, anyone can do it in just a few minutes using the free and open-source AI model, for less than the cost of a cup of coffee, and that's exactly what threat actors are doing. We created ExploitTotal to give defenders the advantage by allowing them to obtain these exploits first, thus gaining the upper hand against cybercriminals."
Microsoft fixed 1,411 vulnerabilities during "Patch Tuesday" in October 2026, a number that exceeds that of the entire year of 2025. Meanwhile, according to the Verizon "2026 Data Breach Survey Report," the median time for organizations to fix vulnerabilities that were being actively exploited was 43 days, and only 26% of those vulnerabilities were completely fixed. On the other hand, vulnerability exploitation activities are surging. The Google Threat Intelligence Group report indicates that there were an average of 18 vulnerability exploitation cases per month in 2026, which is nearly twice as many as in 2025.
Anyday Security indicates that it uses the same type of model as the AI attacker. The company provided more than 200 known vulnerabilities to GLM-5.3, which included some of the most difficult targets to attack in the security field, involving widely used browsers and operating systems; the information provided to the model was limited to what attackers could obtain on the day the repair announcement was released, namely the public description of the vulnerabilities by the manufacturers and the patches themselves. Subsequently, Anyday compared each successfully generated vulnerability exploit with the National Vulnerability Database of the United States, the catalog of known exploited vulnerabilities from the US Cybersecurity and Infrastructure Security Agency (CISA), as well as public vulnerability exploit code libraries, and found that 72% of them had never been publicly exploited before. In one demonstration, this model was able to construct a complete and usable full-chain browser vulnerability exploit in just a few minutes at a cost of less than $1.
Anyday Security, co-founder and chief technology officer, and Omri Sibony stated: "A security team is aware of thousands of vulnerabilities in their environment, but hardly any of these vulnerabilities come with available exploits. Our system generates exploits on the same day that the vendor releases a fix, allowing the team to test those vulnerabilities on their own systems and see if existing tools can prevent such attacks. If not, the team can then write detection rules or virtual patches for real attacks, rather than waiting until an intrusion occurs to discover the problem. Attackers always act first, and we are helping security teams to stay one step ahead."
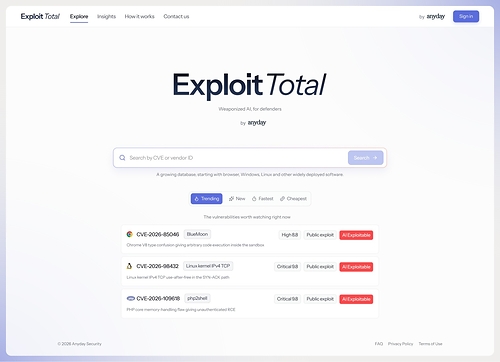
On each vulnerability page of ExploitTotal.ai, a conclusion is provided first, indicating whether the AI model can be used to weaponize the vulnerability, the cost and time required to build a vulnerability exploit, as well as the model that generates the best results. Each vulnerability exploit is rated according to a five-level scale, ranging from merely causing the target program to crash to gaining complete control over it. The page also displays the severity of the vulnerability and whether there are any publicly available exploits; each result is labeled with the model used and the date. Therefore, this directory can also be used to track the speed at which the ability to exploit AI vulnerabilities improves. Anyone can search the ExploitTotal.ai directory for free. Logged-in users can view the complete AI availability assessments, and verified users can download the unweaponized PoC. These PoC can be run against code with vulnerabilities, but they do not contain harmful payloads. The company states that all PoC are intended for use in authorized testing, research, and defense by security teams, and cover both fixed and publicly disclosed CVE vulnerabilities.
ExploitTotal.ai currently covers the most widely used software in enterprises, including Windows, Linux, Chrome, Firefox, and Edge among others. Anyday Security indicates that as its automation systems continue to operate and new AI models are released, the company will continue to update this directory.
ExploitTotal.ai is now available for free at the URL https :// exploittotal.ai.
About Anyday Security
Anyday Security is committed to building a defense layer for the era of attackers targeting AI to prevent large-scale exploitation of vulnerabilities. The company was founded by veterans from the Israeli military's 8200 unit, Yonatan Gorfung (CEO), and Omri Sibony (CTO), who previously served as the Director of Security Research at SentinelOne. The company is headquartered in New York and has a research and development center in Tel Aviv. For more information, please visit https :// anyday.security.
Media Contact
Hannah Yoken [ email protected ]